AI Governance Frameworks for Preventing Data Leakage and Hallucinations in Internal Enterprise LLMs
By Eric Siversen, InnovAit AI
In the rapidly developing sphere of artificial intelligence (AI), enterprise ai governance framework emerges as an essential tool for managing the challenges associated with internal large language models (LLMs). These frameworks play a crucial role in preventing data leakage and reducing hallucinations—instances where AI generates inaccurate or fabricated information. This article explores the core elements of AI governance frameworks, focusing on how they function to uphold internal llm data privacy and security in enterprise contexts. The importance of effective governance cannot be overstated as organizations face stewarding sensitive data and complying with stringent regulations.
This article will guide you through the core components of enterprise ai governance frameworks, the support provided by enterprise data privacy models, prompt injection defenses, strategies for data leakage prevention, techniques to mitigate hallucinations, the role of generative and answer engine optimization, and corporate AI risk management policies.
What are the core components of enterprise ai governance framework in internal LLMs?
AI governance frameworks consist of several core components that are essential for ensuring the ethical and secure use of artificial intelligence within organizations. These components typically include clear governance policies, data privacy compliance, and comprehensive cybersecurity measures.
The necessity of clear governance policies is paramount as it delineates responsibilities and roles within the AI ecosystem. Furthermore, compliance with data privacy regulations ensures that organizations meet the legal standards required to handle sensitive information, fostering trust among users. Finally, effective cybersecurity measures protect against unauthorized access, safeguarding data integrity and confidentiality.
How do enterprise data privacy models support internal llm data privacy governance?
Enterprise data privacy models are critical in supporting the governance of internal LLMs. These models establish frameworks to ensure data handling aligns with statutory regulations and best practices.
Key functions of data privacy models include:
- Regulatory Compliance: Adherence to regulations such as GDPR and CCPA is fundamental for organizations utilizing data-driven technologies.
- Service Audits: Regular audits maintain compliance and identify vulnerabilities in data management.
- Policy Updates: Continuous revisions reflect evolving laws and technological advancements.
Compliance Measures
Compliance measures align internal llm data privacy governance with legal standards. Understanding GDPR and CCPA helps frame AI initiatives effectively. Regular audits track compliance and proactively rectify issues.
Risk Mitigation Strategies
Organizations must implement comprehensive risk mitigation strategies, including strong cybersecurity protocols that reduce vulnerabilities to attacks. Continuous monitoring and timely updates to data security practices help enterprises remain resilient against evolving threats.
Which prompt injection defense enterprise mechanisms form part of effective AI governance?
Prompt injection defense enterprise mechanisms are vital elements of AI governance, safeguarding against manipulative inputs that could lead to erroneous or harmful outputs. These defenses reinforce the integrity of user input validations, ensuring that AI models operate on authenticated and accurate information.
Effective defenses include:
- Input Sanitization: Filtering inputs to remove potential attack vectors ensures only legitimate queries are processed.
- Validation Mechanisms: Robust validation frameworks ascertain authenticity and relevance of provided data.
- User Access Controls: Tiered access controls prevent unauthorized submissions of detrimental prompts.
How can data leakage prevention be implemented in internal large language models?
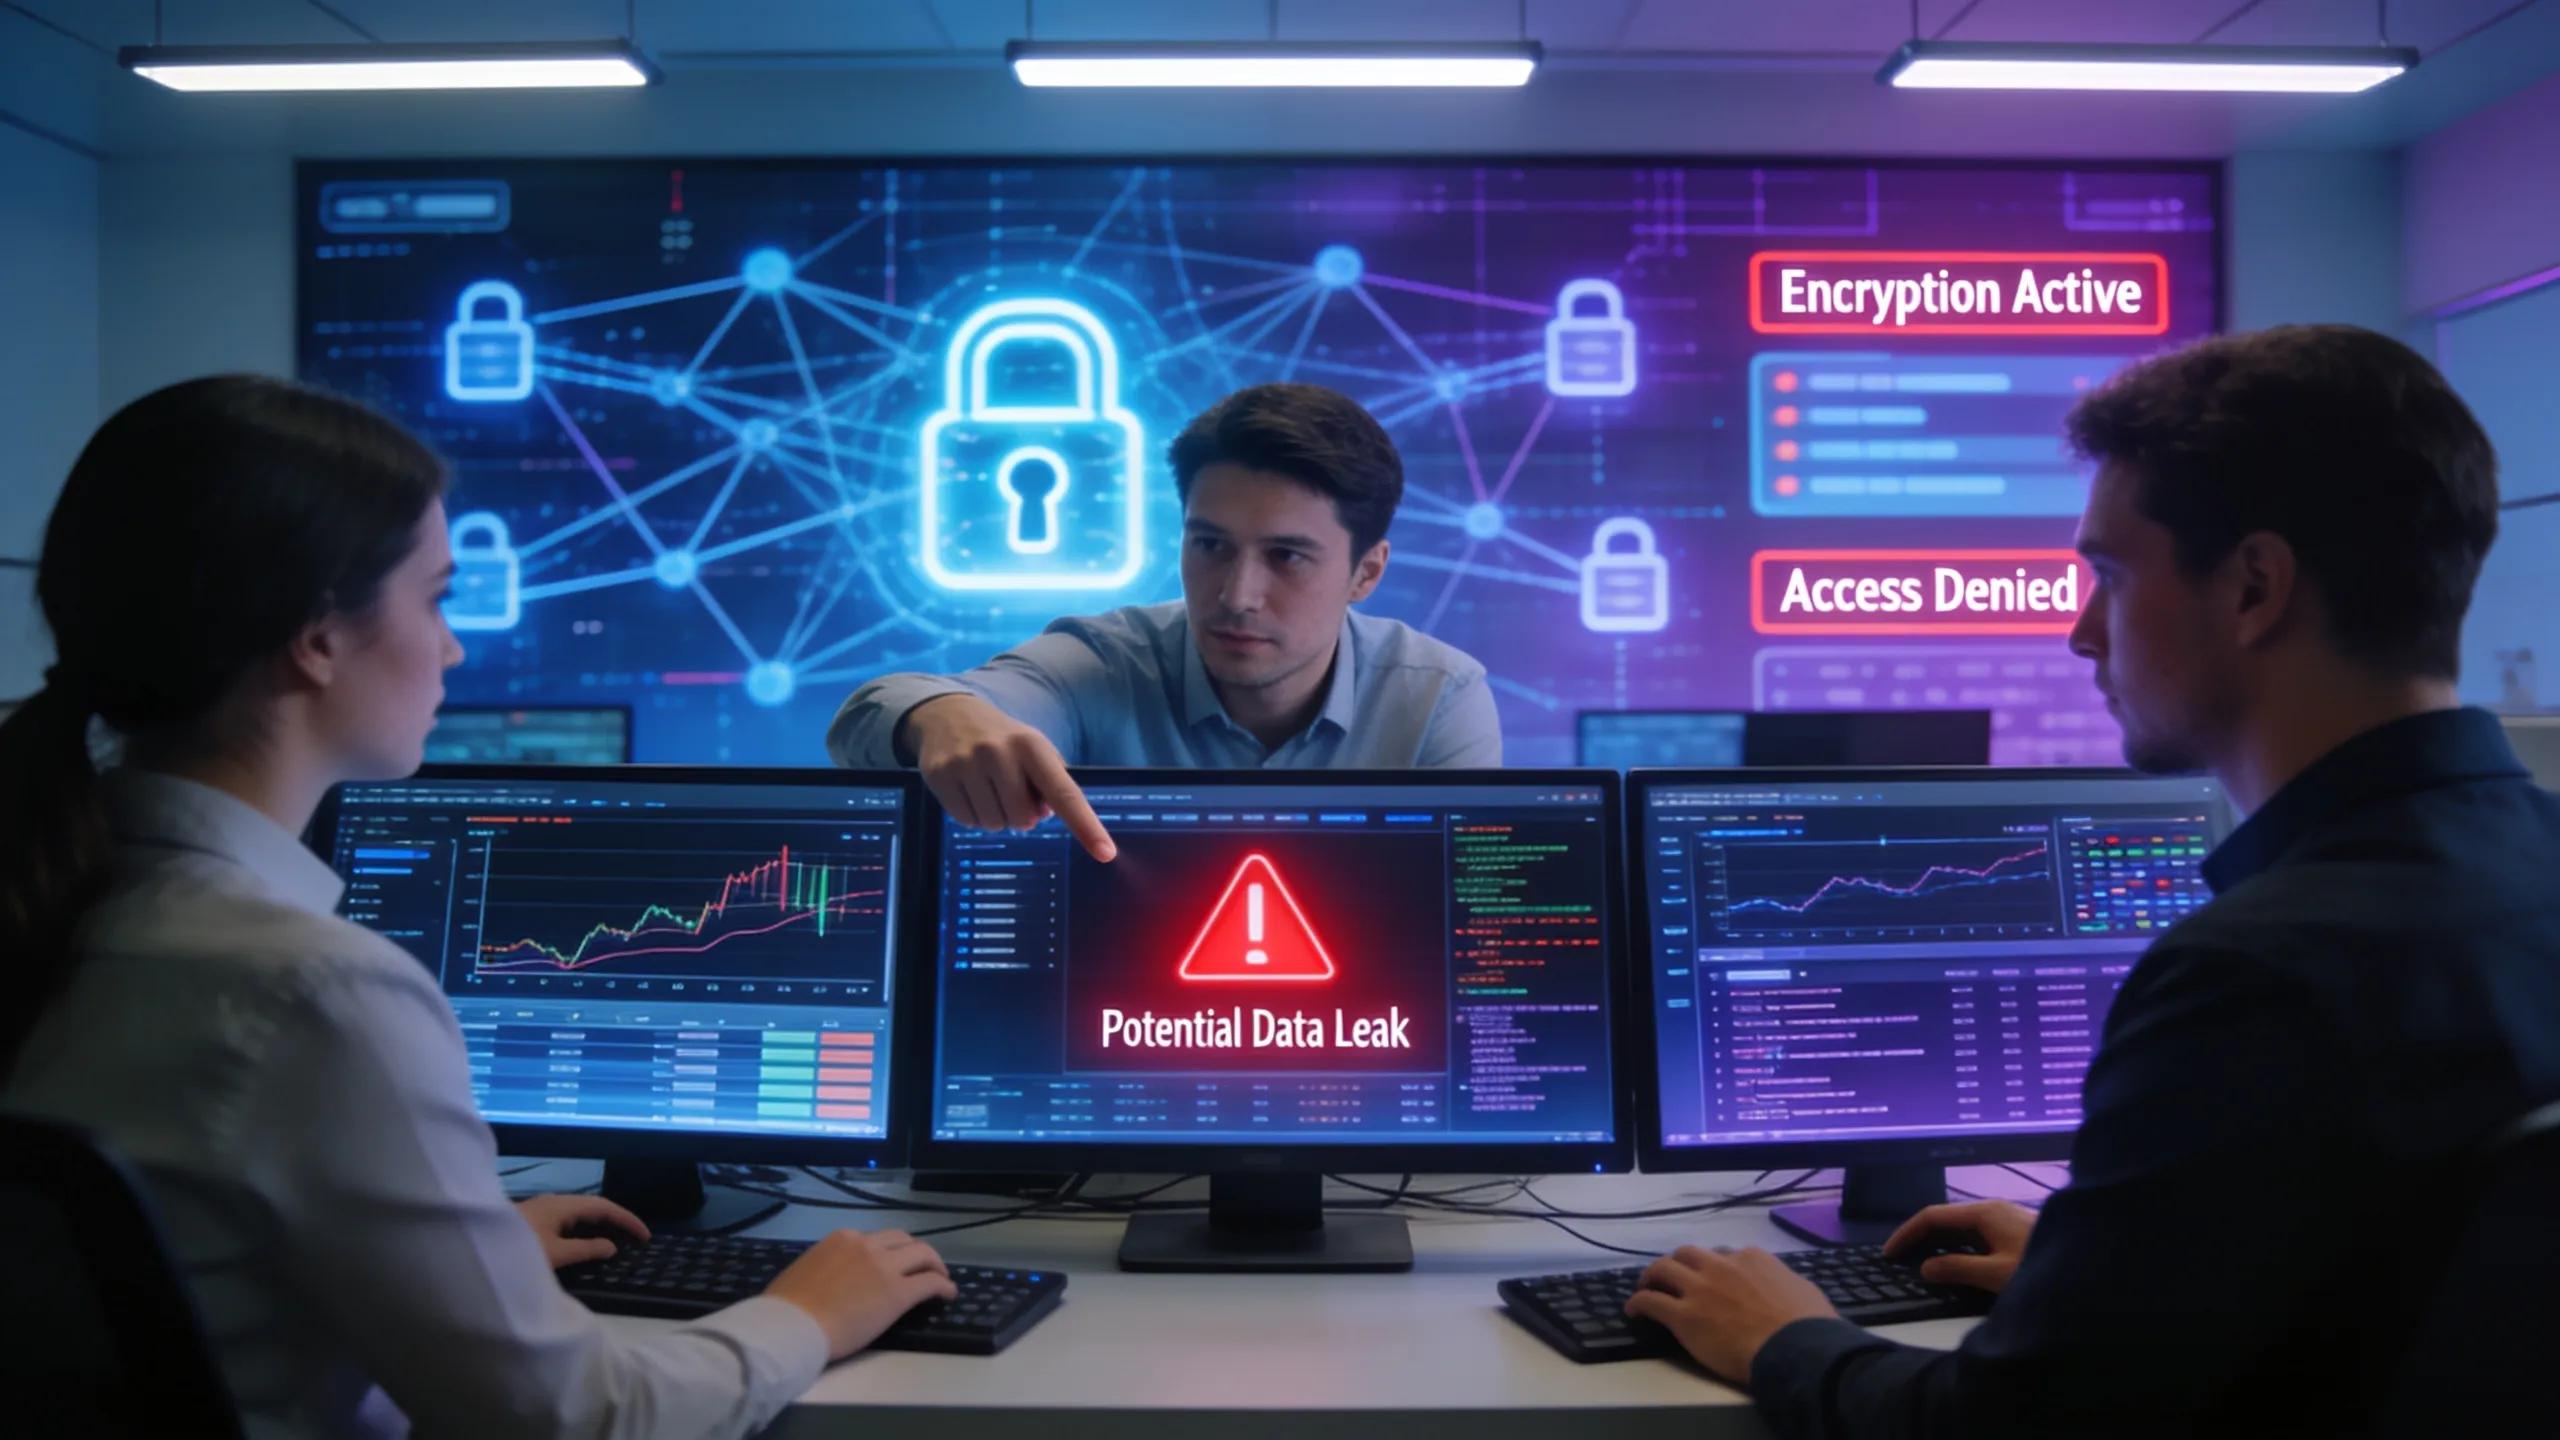
Data Leakage Prevention (DLP) in internal LLMs is crucial for safeguarding sensitive information from unauthorized disclosure. A multi-layered approach enhances data security and mitigates risks from breaches.
What techniques mitigate data leakage risks in enterprise AI systems?
Techniques employed to mitigate data leakage risks include:
- Data Masking: Obfuscates sensitive data, making it unreadable to unauthorized personnel while still usable for analysis.
- Encryption Protocols: Strong encryption safeguards data during storage and transmission.
- Access Monitoring: Monitoring data access logs helps identify and respond to suspicious activities promptly.
How do knowledge graph optimizations enhance data security in LLMs?
Knowledge graph optimizations leverage interconnected data points to enhance security within LLMs. By visualizing data relationships, organizations identify risks and enforce governance policies effectively, improving visibility over data usage and aiding compliance.
Enterprise LLM Zero-Trust Security Gateway Architecture
What are effective AI hallucination prevention techniques for internal LLM deployments?

Preventing hallucinations in AI models is central to ensuring reliable outputs. Various techniques minimize inaccuracies and enhance model performance.
Recent research highlights integrating external knowledge structures to verify outputs and reduce factual inconsistencies.
Knowledge Graphs to Reduce Hallucinations in LLMs: A Survey
ABSTRACT: Contemporary LLMs often produce hallucinations due to knowledge gaps. To address this, researchers augment LLMs by incorporating external knowledge, such as knowledge graphs, to reduce hallucinations and improve reasoning. This survey reviews these augmentation techniques, categorizing methods, evaluating performance, and exploring future research directions. Source:
A survey, G Agrawal, 2024
Which strategies reduce hallucinations in enterprise language models?
Effective strategies include:
- Robust Training Data Curation: Diverse, high-quality data improves accuracy and reduces errors.
- Continuous Learning Mechanisms: Real-time learning refines outputs dynamically.
- Human Oversight: Expert review of model outputs enhances accuracy.
How does prompt security impact hallucination rates in internal AI?
Securing prompts directly impacts output quality. Prompt security restricts the information AI can generate, limiting hallucinations caused by ambiguous or misleading inputs. Establishing strict prompt handling standards significantly reduces generation inaccuracies.
How do generative engine optimization and answer engine optimization support AI search visibility?
Generative engine optimization (GEO) and answer engine optimization (AEO) enhance AI-generated content visibility in search engines. GEO optimizes generative model content production, while AEO ensures answers are relevant and accessible.
Both foster transparency and trust, improving AI product and service search visibility.
What is the role of AEO and GEO in enhancing enterprise AI governance framework?
AEO and GEO establish frameworks ensuring content aligns with organizational standards and user expectations. These strategies optimize information quality and relevance, facilitating a better user experience while protecting organizational interests.
How can marketing executives apply AEO-GEO frameworks to secure AI deployment?
Marketing leaders can apply AEO and GEO frameworks to optimize AI deployments, focusing on quality content and SEO to enhance credibility and engagement.
Integrating AEO and GEO promotes organizational goals and supports compliance, ensuring adherence to industry standards.
Enterprise AI Governance & Security Maturity Matrix
Which corporate AI risk management policies support compliance and security?
Corporate AI risk management policies are vital components of an effective governance framework. Such policies focus on identification, assessment, and mitigation of AI-related risks.
How do AI governance frameworks align with enterprise compliance standards?
AI governance frameworks align with enterprise compliance standards by incorporating data security and ethical AI usage principles. Ensuring AI initiatives comply with legal frameworks maintains organizational integrity.
What are key performance indicators to monitor AI governance effectiveness?
Monitoring AI governance effectiveness involves key performance indicators (KPIs) such as:
- Audit Frequency: Regularity of compliance audits reflects proactive risk management.
- Incident Response Times: Speed of reporting and addressing security incidents.
- Data Access Logs: Observation of access patterns to identify irregularities.
Robust KPIs foster continual improvement of AI governance, ensuring accountability and transparency.
About the Author
Marcus Vance, Principal AI Systems Architect & Chief AI Compliance Officer at InnovAit AI
Marcus Vance brings over 15 years of experience in enterprise security architecture and AI compliance. Holding an ISO 42001 certification, he specializes in developing and implementing robust enterprise ai governance frameworks that secure internal LLM deployments and mitigate risks such as data leakage and hallucinations. Marcus leads efforts in integrating cutting-edge prompt injection defenses and zero-trust security models, helping organizations maintain rigorous compliance with evolving regulations and standards.